

Google has started rolling out its October 2026 software update to all supported Pixel phones running Android 17. The rollout will continue over the next week in phases, depending on your carrier and device. You'll get a notification when it's ready. Here's everything it has for you.
These three fixes are one big relief
Google's Pixel Community Manager shared news of the October update for Pixels on the official forum. It's rolling out to every supported Pixel running Android 17, including every Pixel from the Pixel 6 series through the Pixel 11 series.
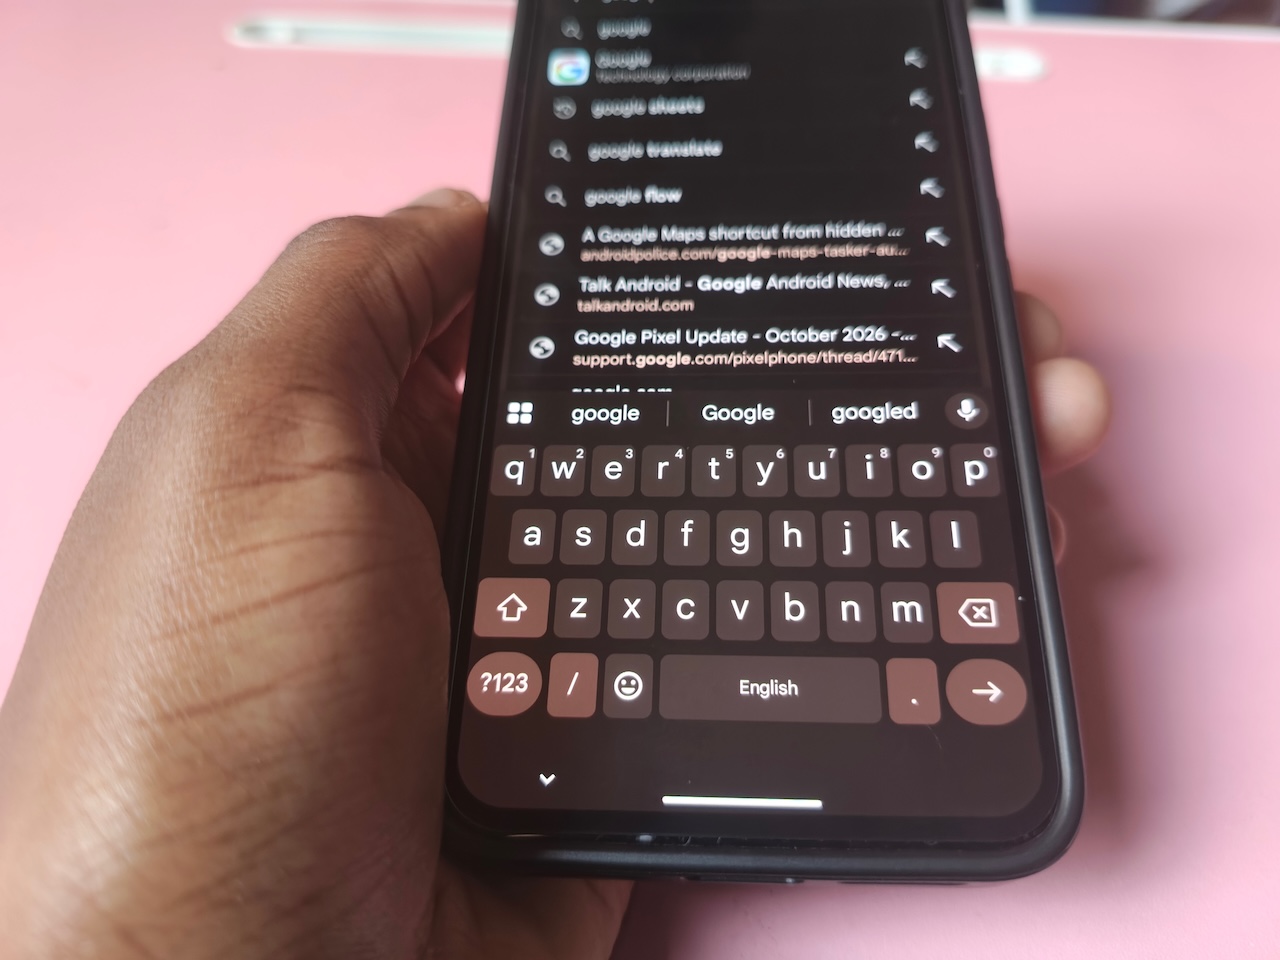
Also on the list are the A-series phones, the Pixel Tablet, and all Pixel Fold models. The update brings three fixes, and the first stops the virtual keyboard from sometimes failing to appear when you tap a search field on the Pixel 8 series and newer.
The second fixes occasional noise or distortion in ringtones during some Voice over IP (VoIP) calls, which covers apps that place calls over the internet. This applies to the Pixel 8 through Pixel 10 series.
The third fixes photos and videos sometimes saving in the wrong orientation, and the fix only applies to the Pixel 11 series. There are also security fixes covered separately in Google's Pixel Security Bulletin.
The update's build numbers show Google shipping three builds. The Pixel 6, Pixel 7, Pixel Tablet, and original Pixel Fold get CP3A.261005.002.A1. The Pixel 8, 9, and 10 series, including the Pixel 10a, get CP3A.261005.005.
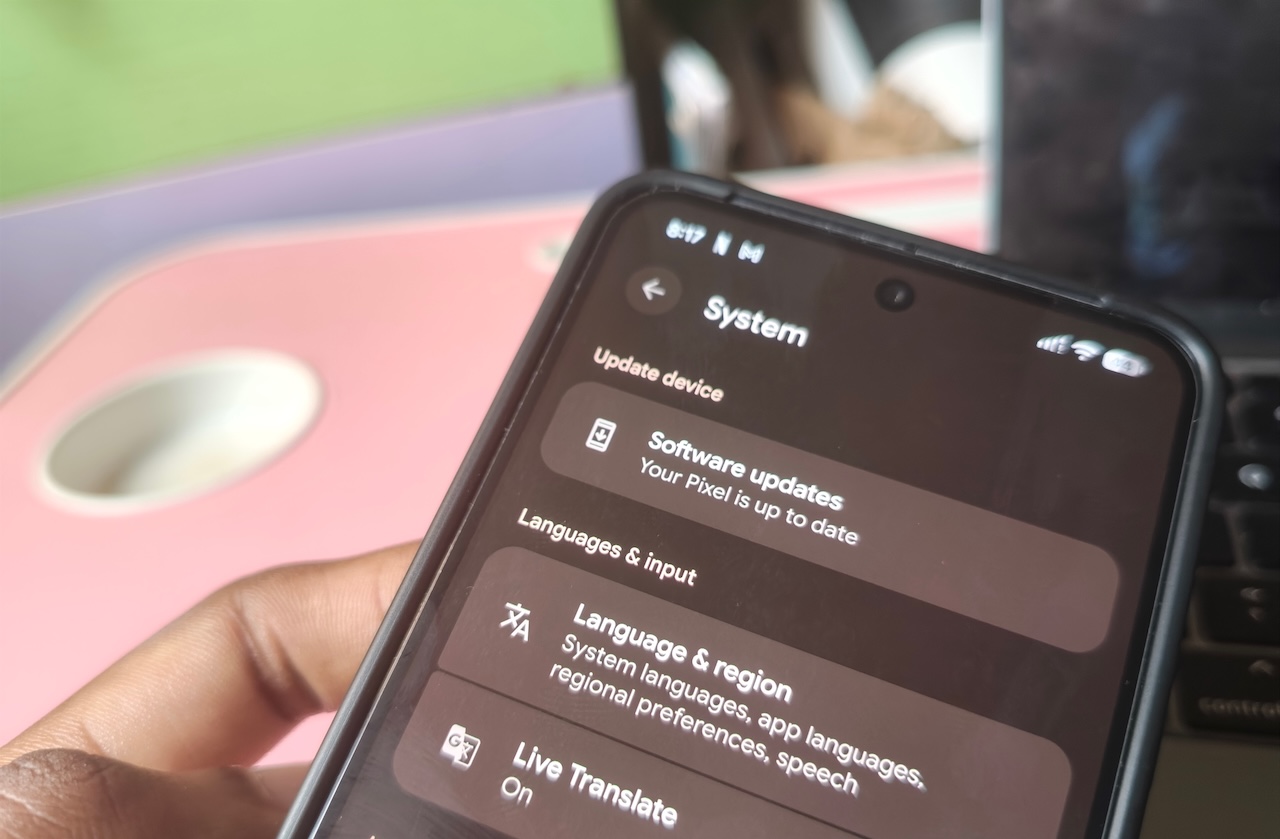
The Pixel 11 series gets CD1A.261005.003, while Pixel 11 units sold through SoftBank in Japan get a version ending in B1. To install it, go to Settings > System > Software updates.
Your Pixel's Bluetooth needed an urgent fix
Google's October 2026 Pixel Security Bulletin details patches for six vulnerabilities on Pixel phones, alongside the wider Android security fixes.
Three are rated Critical, including a Bluetooth flaw that could let an attacker gain more control over your phone. Another gives the same kind of access through the GDMC component, while the third appears in the GSA component.
In particular, the Bluetooth flaw (CVE-2026-55330) is an elevation of privilege (EoP) bug in the Pixel Bluetooth stack. EoP bugs let code run with more permissions than it was granted, potentially reaching system-level privileges.
The stack itself is a high-value target because it parses packets from nearby devices constantly, and usually before any user interaction. Past Bluetooth flaws, like BlueBorne in 2017, were exploitable by attackers within radio range.
Google hasn't said whether this one needs an adjacent attacker, a malicious paired device, or a local app as its entry point.
The other three vulnerabilities are rated High. Two are EoP bugs in the kernel, one in the file system and one in the Wacom pen and touch driver. The third is an information disclosure bug in the GDMC component (CVE-2026-0198), the same component behind one of the Critical flaws.
Google hasn't released technical details for any of the six, but each bug ID carries an asterisk, meaning the fix ships inside Pixel's closed-source binary drivers. Custom ROM users can't pull these fixes from AOSP and will need Google's updated vendor images.
